



Solana’s plan to retire sturdy nonces, which let transactions be signed offline and broadcast later, would protect cold-key approval whereas altering which addresses management the affected belongings. For exchanges, custodians and treasury operators utilizing that signing technique, the proposed alternative provides a program between the chilly key’s approval and execution.
The Solana Basis’s October deprecation plan factors to onchain signer packages that confirm an offline signature and execute its accepted directions. A program-derived tackle, or PDA, would management the affected accounts. The unique key would nonetheless authorize actions, whereas a separate on-line operator submits them and pays the community charge.
The alternative creates a distinct custody structure: operators should migrate the related belongings or permissions, functions should settle for actions arriving by means of one other program, and threat groups should approve the brand new signing path.
Sturdy nonces stay usable. The Basis has not set a elimination date or made a ultimate alternative between Anza’s Programmatic Signer and Blueshift’s Vector. Its roughly six-month migration window is conditional on an appropriate alternative being prepared, audited and stay on mainnet.
The important thing retains approving, however the account adjustments
Sturdy nonces remedy a timing downside. As an alternative of signing a transaction tied to a current blockhash that quickly expires, an offline signer can approve one utilizing a saved nonce. That enables approval and broadcast to occur at totally different instances.
Solana’s separate 200ms slot improve reached its ultimate mainnet stage on Oct. 9. Sooner block manufacturing leaves much less wall-clock time for unusual blockhash-based approvals, though expiry will depend on block manufacturing somewhat than a assured timer. CryptoSlate’s earlier protection examined that timing change; the nonce proposal issues the structure used to keep away from the quick approval window.
Solana doubles block production speed to 200ms as network prepares for Alpenglow upgrade
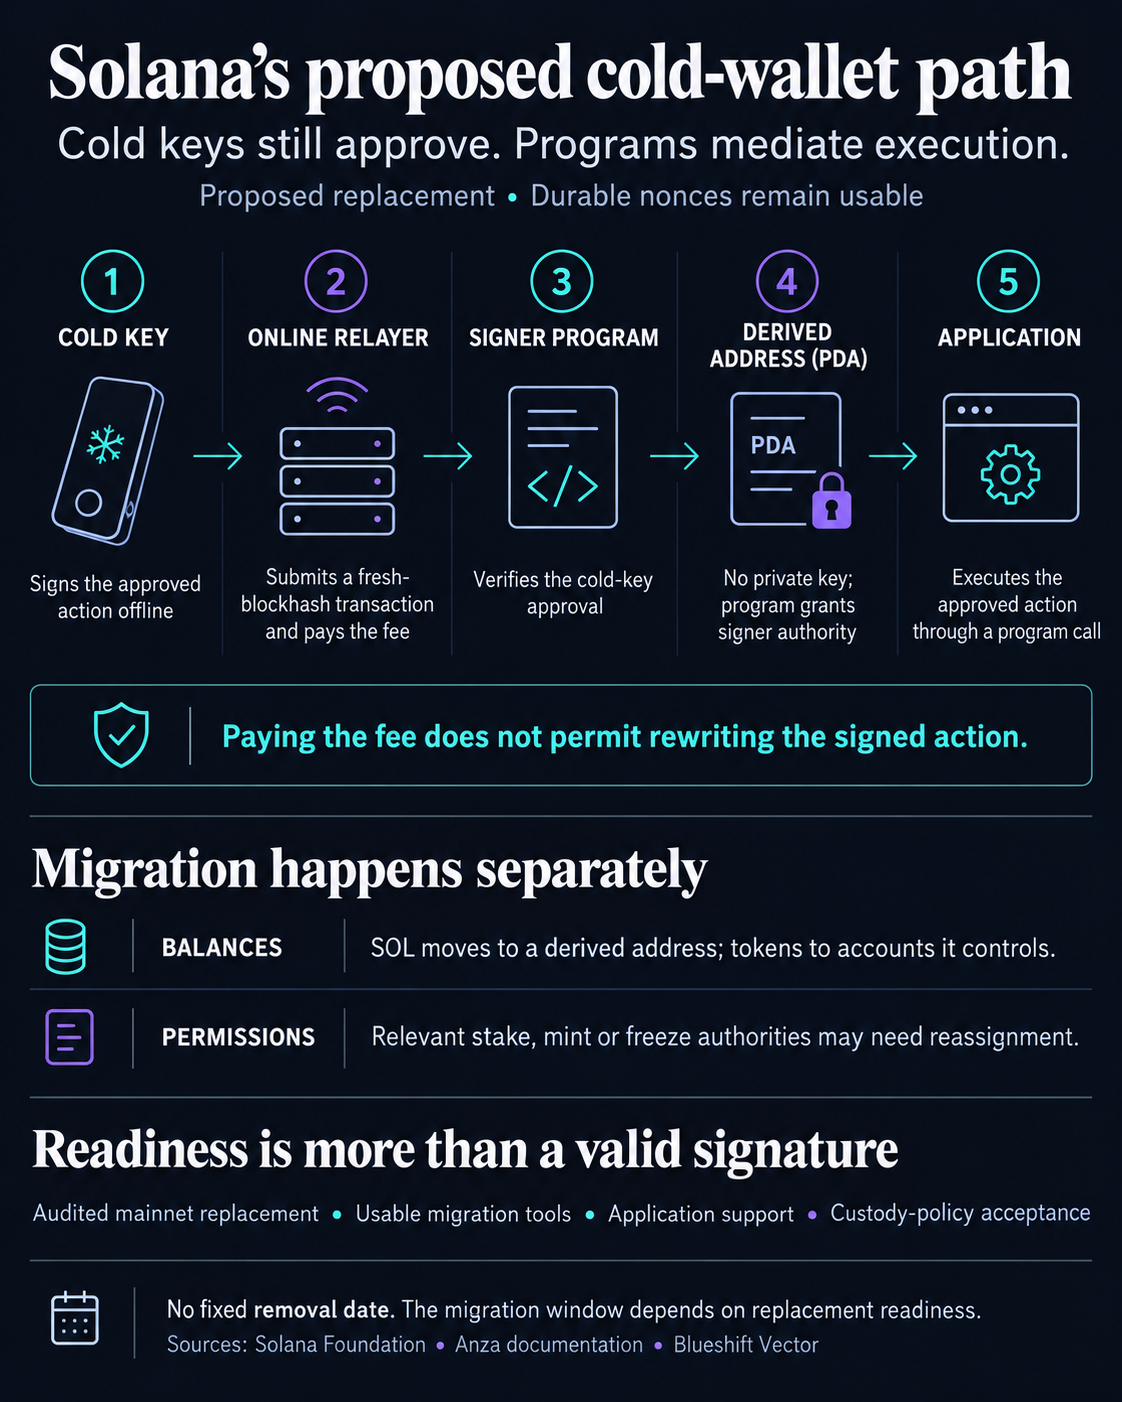
Underneath Programmatic Signer, the chilly key indicators an authorization message somewhat than the transaction despatched to the community. A relayer locations that approval in a fresh-blockhash transaction. The signer program verifies the authorization and executes the accepted directions with the important thing’s derived tackle as signer.
The PDA has no non-public key of its personal. Its means to behave comes from the signer program verifying the unique key’s approval. Deriving the tackle doesn’t transfer any belongings or permissions: these have to be transferred individually.
The migration information describes transferring native SOL into the derived tackle, transferring token balances into accounts managed by it, and transferring mint or freeze permissions to it. Stake accounts can transfer the staker authority, withdraw authority or each, relying on the permission being migrated. These are separate controls, somewhat than one common pockets change.
The Basis proposes finishing these handoffs whereas legacy sturdy nonces nonetheless work. For an affected treasury, approving the brand new signing software program is subsequently solely a part of the job. Its account stock and the permissions every key at the moment holds decide what should change.
The 2 candidate designs additionally deal with native SOL in a different way. Programmatic Signer’s derived SOL account is System-owned and might ship SOL by means of an accepted unusual switch. Vector initializes a program-owned account and releases SOL by means of its personal approved withdrawal or closing operation.
What the chilly signature lets a relayer do
The implementation alternative impacts how tightly an approval constrains the transaction round it.
Programmatic Signer’s message documentation says the chilly signatures bind the executor, nonce account and embedded execution message. A relayer can’t alter these approved bytes whereas retaining legitimate signatures. It may, nevertheless, select the outer charge payer and blockhash and add directions earlier than or after the submission.
Vector commits to the top-level instruction buffer, together with the info and accounts used to cross accepted actions into different packages. Directions surrounding these actions should already be included when the chilly key indicators. A relayer can’t insert, take away or reorder them afterward with out invalidating the approval.
Programmatic Signer permits an execution context to be assembled round an accepted motion; Vector requires the encircling instruction sequence to be accepted prematurely. In each instances, paying for broadcast doesn’t grant permission to rewrite the signed motion.
| Management | Programmatic Signer | Vector |
|---|---|---|
| Chilly approval covers | The authorization and embedded execution message | The dedicated top-level instruction buffer |
| Additional surrounding directions | Relayer might add them exterior the authorization | Have to be included earlier than signing |
| Replay state | A separate program nonce account | Nonce saved within the Vector account |
| Derived-address setup | No signer-address registration | Account initialized beneath the Vector program |
A failed execution try can depart a chilly approval executable later. A present durable-nonce transaction that passes validation however fails throughout execution nonetheless consumes its nonce. Programmatic Signer’s structure commits the nonce advance and software adjustments collectively, or rolls them again collectively. Vector paperwork the identical means to retry a failed motion.
For operators, retryability means a failed submission has not essentially invalidated the approval. With out an enforced deadline, it might probably stay obtainable for later execution whereas its nonce is unchanged.
Vector explicitly warns {that a} relayer might withhold a transaction till circumstances change, or {that a} signature uncovered by a failed try might execute later. A timeout included within the signed directions can reject execution after a deadline. Revocation requires a individually approved nonce advance to land. A deadline rejection itself doesn’t eat a nonce whose adjustments roll again with the failed transaction.
Utility entry is a separate custody take a look at
The Basis’s rationale is to simplify validator dealing with. Sturdy nonces require particular replay-prevention guidelines, complicate asynchronous execution and make invalid transactions tougher to filter. Shifting approval and replay state into unusual packages leaves validators processing regular blockhash transactions.
Purposes then obtain accepted actions by means of cross-program invocation, or CPI: one program calls one other. That may battle with an software’s rule that an motion should arrive instantly as a top-level instruction. Checks that examine solely top-level compensation or signature-verification directions also can miss an motion nested contained in the signer program.
Extra obtainable name depth doesn’t resolve a rule that rejects the decision’s place or can’t examine the nested directions. The Basis suggests supporting identified signer packages or providing one other execution path. Whether or not an software accepts a PDA’s signature is consequently a distinct query from whether or not the offline approval is cryptographically legitimate.
Solana triples transaction size as major upgrades meet record network activity
Token-2022’s CPI Guard exhibits why compatibility wants a exact account-level evaluation. With the guard enabled, CPI transfers and burns require delegate authority; approvals by means of CPI are prohibited, and altering the proprietor is prohibited even exterior CPI. Everlasting delegates have switch and burn exceptions.
These guidelines are extra particular than a blanket ban on each PDA motion. A delegate-based switch route might exist, however establishing or utilizing that authority introduces its personal permission and custody-policy resolution.
Institutional issues raised in March centered on software entry and the controls beneath which funds might transfer. Within the March 4 dialogue, a participant figuring out himself as Michael from Fireblocks supported nonce deprecation whereas objecting to CPI Passthrough’s migration, contract dependence and DeFi compatibility burdens. He favored transaction envelopes, with Sudo in its place, somewhat than the proposed CPI-based signing path.
Grant, who recognized himself as being at Unit 410, mentioned the identical day {that a} small, auditable signer program may make authority migration acceptable. He rejected a workaround that briefly strikes belongings to a scorching signer, even for an atomic operation, as a result of funds should stay related to chilly storage in its noncustodial mannequin.
Solana DvP settlement requires 100% upfront cash for every trade
A testable design nonetheless wants a manufacturing migration path
Programmatic Signer’s present documentation stories devnet deployment and audits in progress, with remediation required earlier than its v1 launch and any mainnet deployment. Its interfaces might change. The utilization documentation nonetheless marks simulation and relay submission as coming quickly, whereas a number of migration operations are equally unfinished within the information.
Vector publishes implementation code and program IDs; its README doesn’t state an audit or mainnet deployment standing.
In the meantime, Fireblocks’ present protocol onboarding package nonetheless describes automated durable-nonce injection for chosen WalletConnect integrations, together with Jupiter and Kamino, with a default provider-managed 15-minute validity window. That describes an present approval workflow which a alternative should accommodate.
An operational migration wants an audited mainnet alternative, usable instruments and software paths that retain every operator’s approval controls.
The submit Solana’s offline-signing proposal would maintain approvals legitimate after failed transactions appeared first on CryptoSlate.