


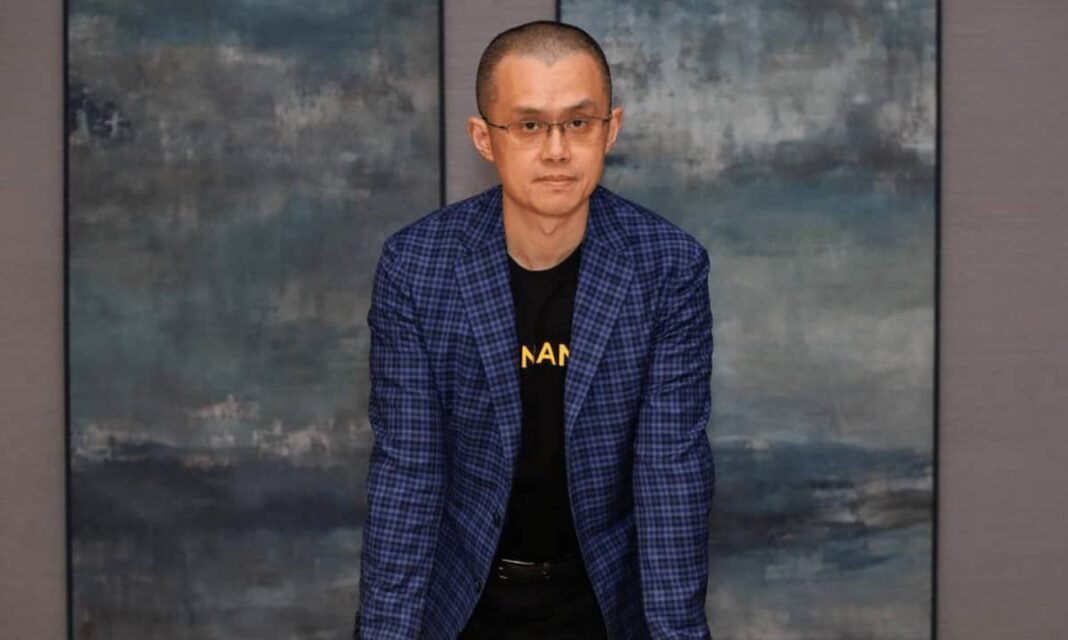

Binance co-founder Changpeng Zhao (CZ) has urged iPhone customers to replace their working programs amid warnings that the DarkSword exploit can steal crypto pockets info by compromised web sites.
The menace has raised considerations about self-custody safety, particularly contemplating that the reported assault is alleged to have the ability to goal delicate gadget knowledge even with out victims connecting their wallets or approving transactions.
DarkSword Exploit Places iPhone Crypto Wallets at Danger
In a November 6 put up on X, CZ informed customers to put in the most recent iOS updates, particularly those that haven’t up to date their gadgets shortly. Moreover, he reminded crypto holders that pockets apps can not replace a cellphone’s working system.
“No pockets software program can replace your OS,” he wrote. “Self-custody means self-responsibility.”
His warning got here within the wake of studies that DarkSword can exploit vulnerabilities on iOS by malicious web sites opened in Safari. Discussing the menace, a crypto consumer identified that an assault wouldn’t even want a pockets connection, transaction signature, or approval, with only a easy go to to an contaminated web site being sufficient to reveal delicate info reminiscent of pockets recordsdata and restoration phrases saved within the gadget.
Officer’s Notes, a menace researcher, had earlier reported that about $5.57 million value of crypto had already been stolen by the vulnerability, with greater than 18 web sites allegedly concerned in distributing the malicious code.
Based on the account, DarkSword was being offered on-line for $30,000, and the vendor has listed iOS 18.6.2 as the most recent supported firmware. As well as, researchers have reportedly discovered placeholders for iOS 26 and 27, which may counsel that the infrastructure is being ready for potential exploits sooner or later.
Nevertheless, Officer’s Notes identified that Apple had already patched all vulnerabilities, numbering six, that had been used within the recognized exploit chain. That stated, the wallet-targeting code remains to be related because the researcher says they found that elements of the older model may nonetheless be reused, with one iteration that includes a devoted perform for the imToken pockets.
iOS Vulnerabilities Uncovered Crypto Holders within the Previous
There have been different iPhone safety incidents that resulted within the stealing of crypto, together with a vulnerability in Apple’s 2D rendering engine, CoreGraphics, which allowed malicious code to run when a particularly crafted file was processed. The cellphone producer addressed the difficulty with the discharge of iOS 26.7.1 and iPadOS 26.7.1 towards the tip of September.
Nevertheless, it did acknowledge that the flaw might have been exploited in extremely subtle assaults towards particular individuals, with safety agency SlowMist on the time warning crypto customers to replace their gadgets and to keep away from suspicious hyperlinks and downloads.
There was additionally one other case that concerned the FomoPeek app, the place SlowMist and OKX safety reportedly discovered malicious code within the app that might exploit iOS weaknesses and entry delicate info past FomoPeek’s regular permissions.
The put up CZ Urges iPhone Customers to Replace iOS Amid DarkSword Risk appeared first on CryptoPotato.