


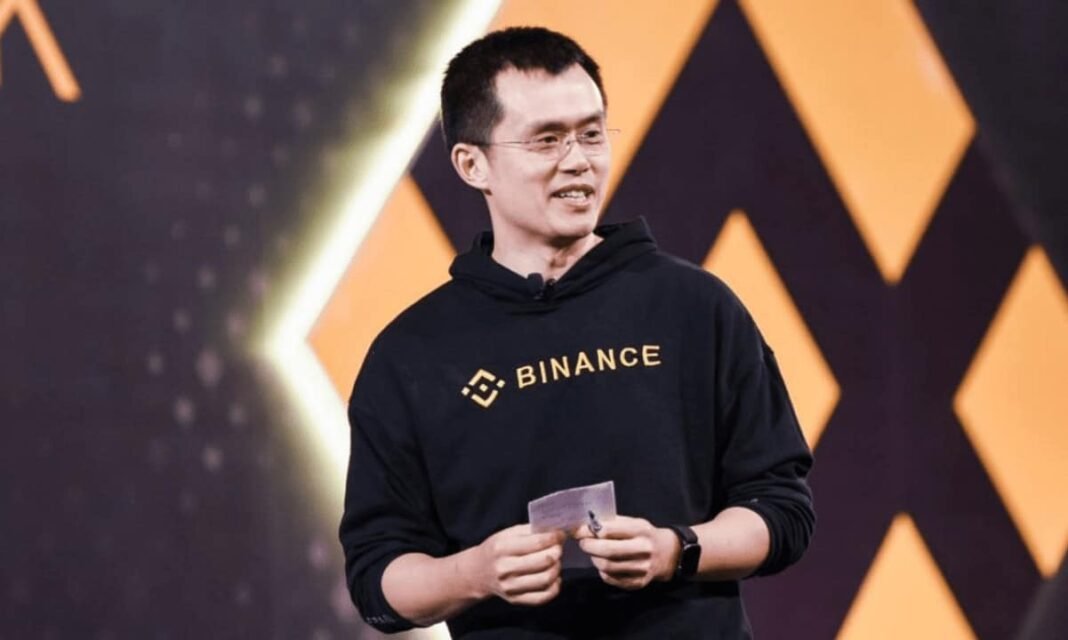

Changpeng Zhao (CZ) is telling web customers to be additional cautious on any web site for the subsequent few days, after two PHP vulnerabilities have been patched on October 21 when their particulars leaked early.
As a result of attackers want no login to use them, a website somebody merely visits might turn out to be a path to stolen credentials or a compromised system, CZ warned.
Exploitation Confirmed within the Wild
In an October 21 submit on X referring to vulnerabilities CVE-2026-109618 and CVE-2026-109619, Zhao wrote:
“Name me paranoid, however be additional cautious visiting ANY website within the subsequent few days, as some internet admins usually are not all the time up-to-date with safety patches.”
NSA Cyber suggested organizations working PHP to arrange for an replace and to take the affected system offline if patching couldn’t occur instantly. The FBI’s cyber division repeated the offline choice and requested operators to observe for PHP processes that unexpectedly launch command shells. Cloudflare acknowledged that it had switched on default firewall protections earlier than the failings grew to become public.
In keeping with a PHP Basis weblog submit, the 2 CVE numbers started circulating on-line on October 20 with a fallacious launch time and a severity rating of 10.0 as an alternative of the true 9.2, although no technical particulars have been out.
Calif, one of many companies that reported the bugs, then mistakenly revealed a proof-of-concept video, and Chainguard launched patch photographs greater than six hours forward of the agreed time. Curiously, the inspiration famous that no purposeful exploits had been discovered when the discharge went out, whereas CZ’s submit describes assaults confirmed afterward.
“Exploitation was confirmed within the wild quickly after disclosure, prompting fast WAF protections and patching by IT groups, as unauthenticated assaults might flip visited websites into vectors for credential theft or system exploits,” acknowledged the Binance founder.
BNB Chain and PancakeSwap Say Their Programs Are Unaffected
The warning doesn’t imply each cryptocurrency platform is susceptible. BNB Chain govt Nina Rong confirmed that the community doesn’t use PHP in its know-how stack, whereas decentralized change PancakeSwap posted that it doesn’t use PHP anyplace in its infrastructure and that consumer funds have been protected.
Zhao subsequently reposted PancakeSwap’s assertion, commenting that “Most tasks ought to a minimum of submit a affirmation like this.”
In the meantime, OpenAI acknowledged that its fashions helped researchers discover the bugs by its Patch the Planet initiative and referred to as the bug “probably the most impactful vulnerabilities in current reminiscence.” To its information, the corporate added, frontier AI bought to the issue forward of attackers.
Ethereum co-founder Vitalik Buterin has pushed the concept that AI hacking makes cybersecurity hopeless, reasoning that AI in a position to present laborious math theorems might additionally show a program safe.
The submit CZ Warns Crypto Customers as Crucial PHP Vulnerabilities Put Web sites at Danger appeared first on CryptoPotato.